
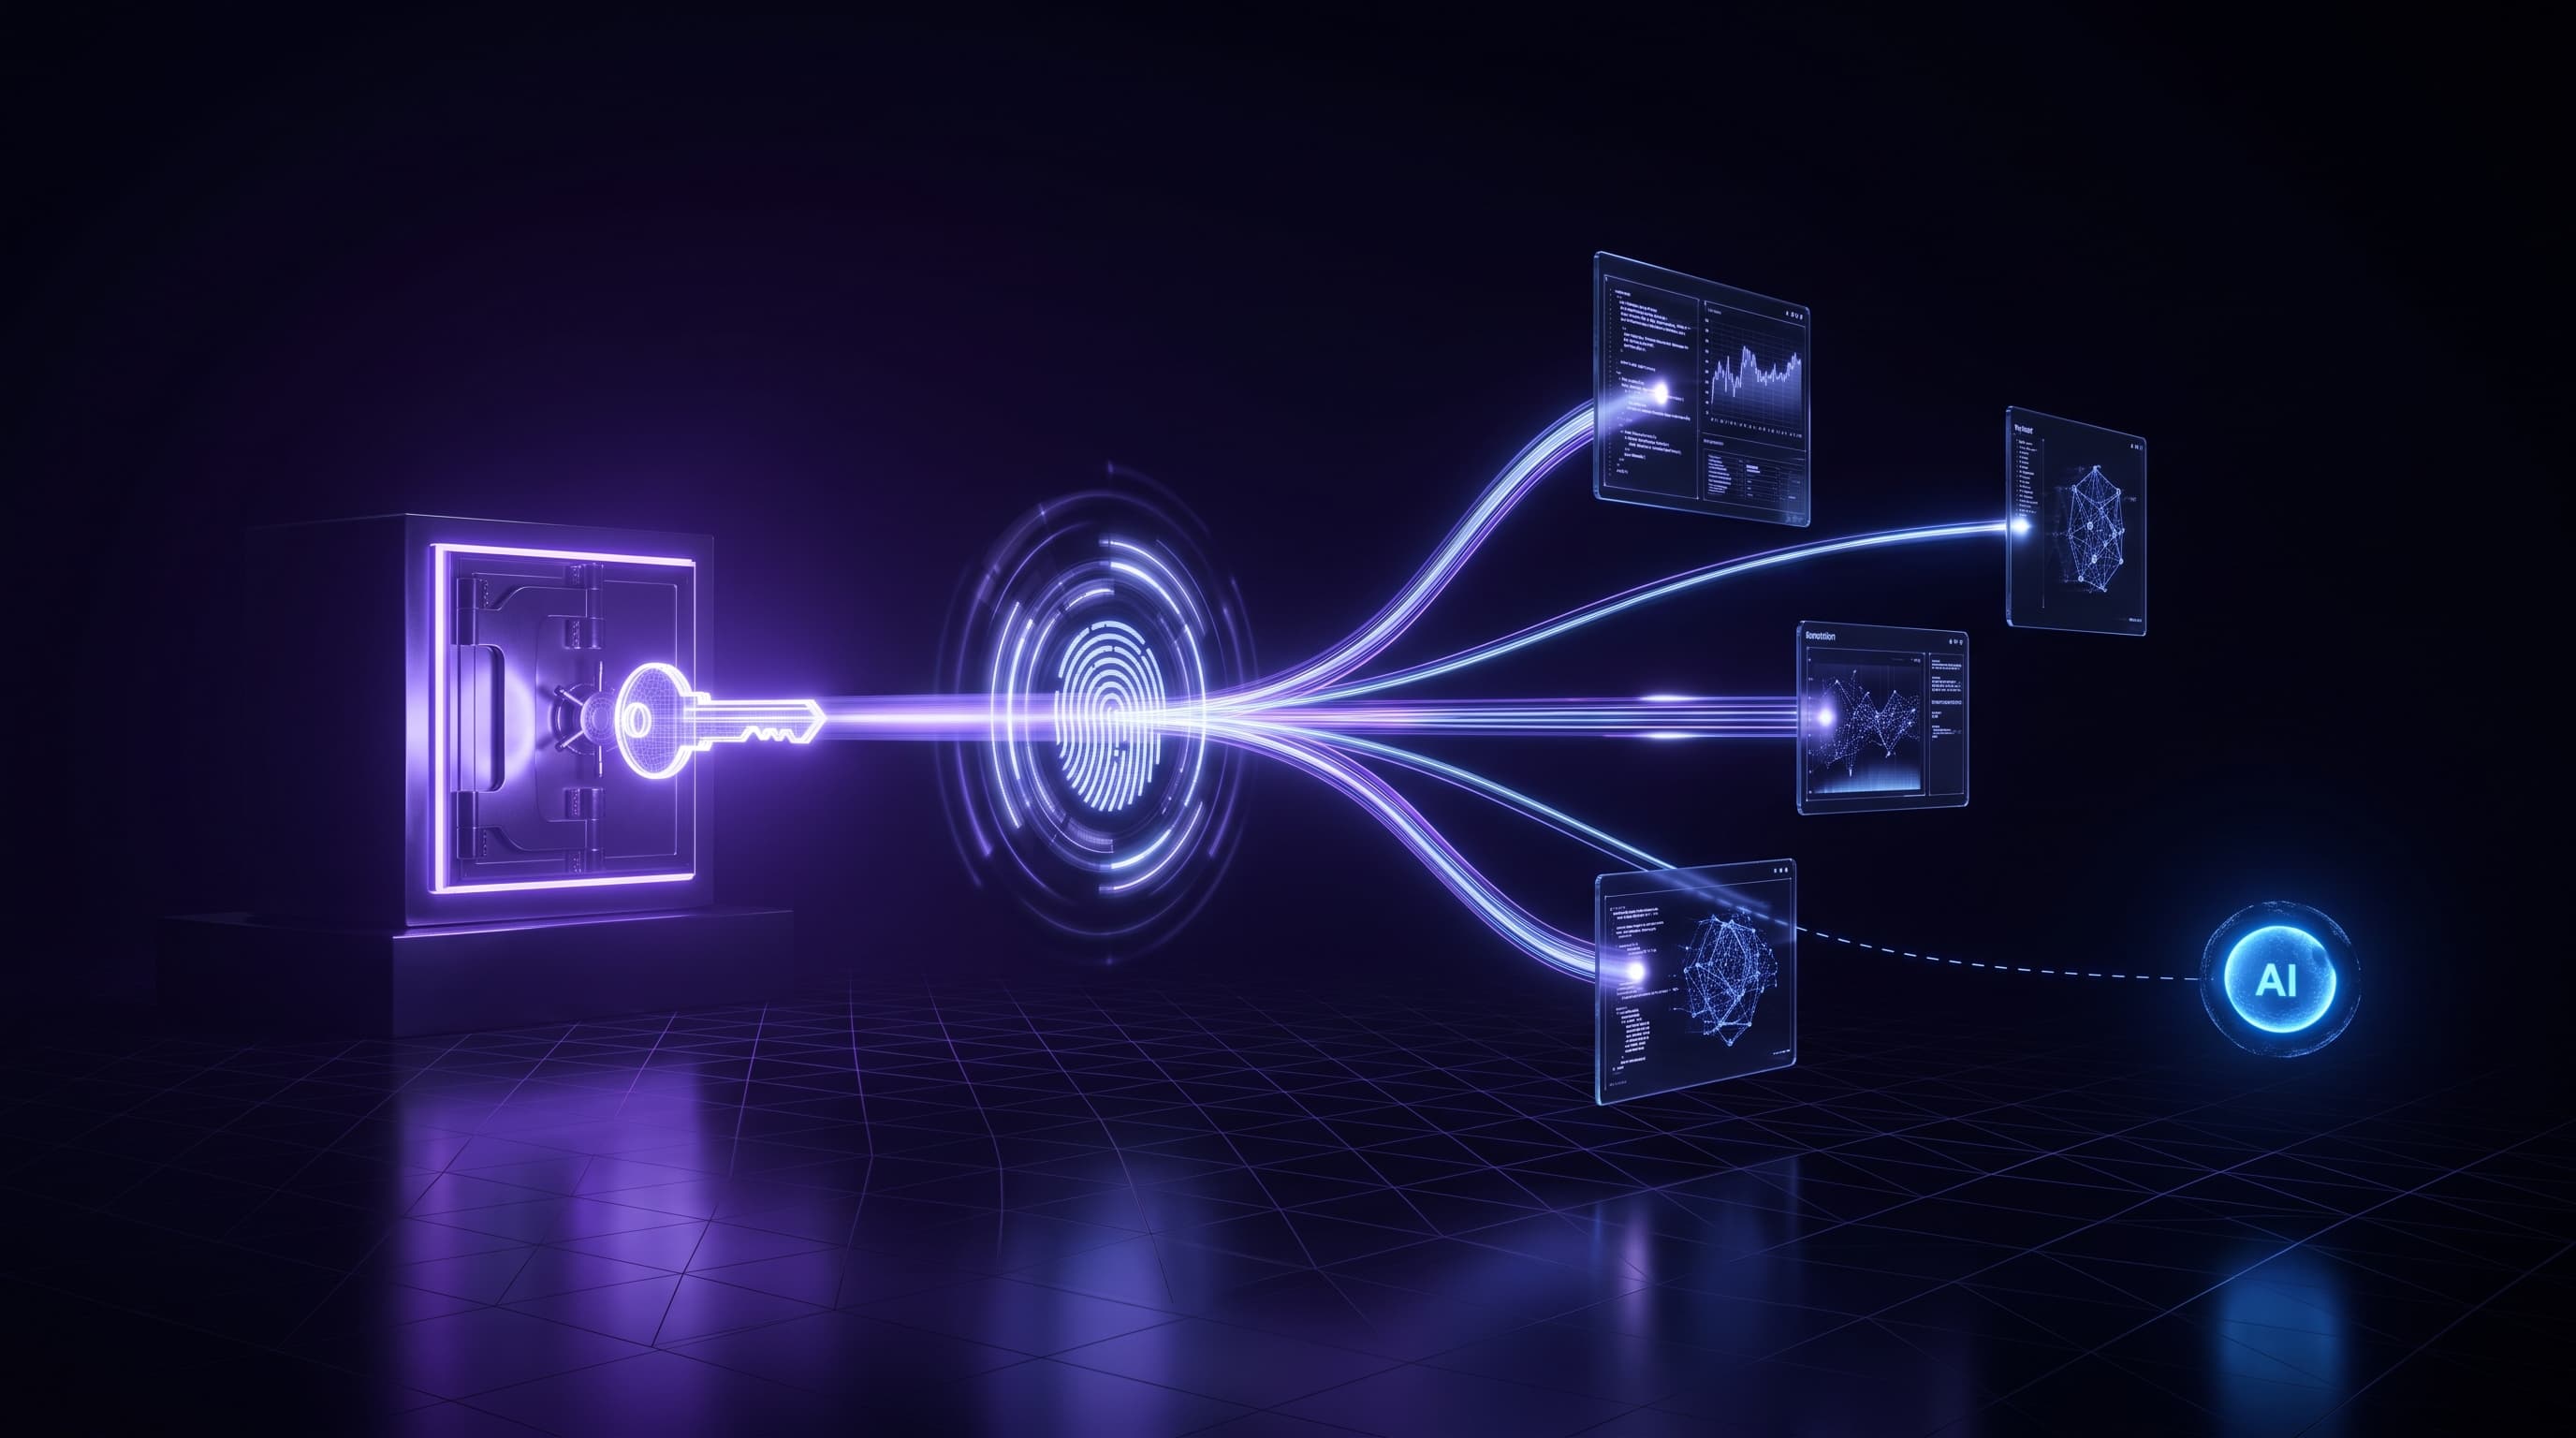
Updated August 31, 2026: Secret references reduce plaintext exposure, but the final process can still read an injected secret and agents can cause tools to use it. The security boundary depends on process isolation, permissions, logs, approvals, and tool design—not 1Password alone.
Agents that call APIs or business systems need credentials. Pasting them into prompts, source files, or logs is dangerous. Properly configured, 1Password can resolve secret references at runtime so raw values do not need to appear in agent instructions. ITECS uses this pattern as one control in custom AI agent deployments.
With the 1Password CLI, configurations can store references while an authorized runtime receives the resolved value. Biometric approval may be used where the platform and workflow support it. Treat the destination process and every child process as trusted for that secret, and log metadata without logging the value.
The Problem: AI Agents Need Secrets, but LLMs Should Never See Them
An AI coding agent that opens pull requests needs a Git token. An agent that checks your tickets needs your PSA's API key. An agent that reads a hypervisor needs its credentials. The moment those secrets live in a plaintext file, a shell history, or a prompt, they are one screenshot, one log line, or one leaked context window away from exposure.
The specific risk with AI is the model itself. Language models are non-deterministic, their inputs get logged, and their context can be retained or leaked. 1Password states the principle plainly: secrets should not be exchanged over a channel driven by an AI model. The fix is to keep the secret out of that channel entirely.
The AI Model (LLM)
Reads your request and the results — decides which tool to call.
↓ Prompts & results only — the secret travels a separate path ↓
1Password Vault
Secrets stored encrypted
Biometric Approval
Touch ID / Windows Hello
Agent / CLI / IDE
Secret injected at runtime
External Systems
PSA · Hypervisors · PAX8
Encrypted secret — injected at runtime, never printed
How 1Password Injects Secrets Without the LLM Ever Seeing Them
The 1Password command-line tool, op, replaces stored secrets with references — short pointers that look like op://vault/item/field. Your config files hold the reference, not the secret. At runtime, op run confirms the CLI is authorized and swaps each reference for the real value, injecting it as an environment variable into the process that needs it.
The secret lands in the authorized process rather than being deliberately placed in the model prompt. That reduces exposure, but a process, plugin, tool, debug trace, crash dump, or agent-chosen command may still disclose an environment value. Use a dedicated least-privilege identity, restrict commands and network access, sanitize logs, and test the exact runtime. This is the discipline taught in our Claude Cowork and ChatGPT Codex training programs.
The Human-in-the-Loop: Biometric Approval on Every Access
Injecting a secret automatically is convenient, but not always safe. 1Password adds a human gate. With the desktop app integration turned on, the CLI authenticates with Touch ID on macOS or Windows Hello on Windows. When an agent reaches for a secret, you approve it with your fingerprint.
Approval can reduce unattended access, but it does not prove that the requested operation is safe or that every access will prompt. Confirm session behavior, approval caching, headless workloads, and what the user can see before approval. Pair the prompt with task-scoped credentials and an auditable tool action.
The Reciprocal Pipeline: Agents That Write Secrets Back
The flow runs both directions. Agents do not just read secrets — they can create them. When an agent provisions a new service, generates an API key, or rotates a token, it can write that secret straight into 1Password using the CLI or the 1Password SDK.
This closes the loop. Instead of a freshly generated key ending up pasted in a chat or a notes file, it is stored, encrypted, and governed the moment it exists. Every credential the agent produces lands in the same vault, under the same access controls and the same biometric gate. Secrets sprawl stops before it starts.
Case Study: How ITECS's Internal Documentation Agent Uses This
ITECS built an internal AI agent that gives our technicians an LLM interface to review, update, and create SOPs, knowledge-base articles, and documentation — the self-hosted agent architecture we described here, extended to live operations.
A technician can ask the agent what tickets are open, what a project's status is, or which licenses a client holds. To answer, the agent reaches into our real systems: our PSA for tickets and projects, our datacenter hypervisors for infrastructure, and PAX8 for license inquiries. Each of those calls needs an API secret.
The design goal is to keep raw secrets out of prompts and repository files. The authorized tool runtime resolves the credential when needed, with approval where supported. Because the destination process can use the secret, access is scoped to the task, tool calls are logged, outputs are reviewed, and credentials remain revocable. That is the pattern ITECS evaluates for client workflows.
How ITECS Architects Secure AI Agent Workflows
We deploy this pattern as a repeatable engagement. The steps are consistent whether it is one developer's IDE or a fleet of production agents.
Step 1: Inventory the secrets. We find every API key, token, and password your tools and agents use — including the ones already pasted in plaintext — and move them into 1Password.
Step 2: Convert to secret references. We replace every hardcoded secret in configs and scripts with 1Password references, so nothing sensitive sits in a file or a repository.
Step 3: Enable biometric approval. We turn on the desktop app integration so each agent's access to a secret requires Touch ID or Windows Hello sign-off.
Step 4: Close the loop and govern. We wire agents to write generated secrets back into 1Password, set vault access controls per role, and enable audit logging so every secret access is recorded.
Security and Governance
This architecture is built on 1Password's own developer tooling. Their documentation on secret references details how the CLI resolves secrets at runtime without writing them to disk. We combine that with vault-level access controls, per-role permissions, and audit logs so you can prove who accessed which secret and when. Before we connect any agent to sensitive systems, we run a data and AI readiness audit to classify what the agent may touch.
None of this is theoretical for us. ITECS has run a Dallas cybersecurity practice since 2002, and we have watched ungoverned AI tooling turn into incidents — the OpenClaw agent security crisis is a recent example. Secrets management is where agent security either holds or fails, and it is the first thing we lock down.
What This Costs and Why It Pays Off
The tooling is inexpensive. 1Password is a per-seat subscription your team may already have, and the CLI is included. The value is in the architecture — configuring secret references, biometric approval, write-back, and access controls so the whole system is secure by default rather than secure only if everyone remembers to be careful.
ITECS prices this the way we price all engineering work: hourly consulting or prepaid retainer hours with tracked usage, a 12-month expiry, plus a flat fee for a scoped secrets-and-agent build. The return is avoided breaches, provable compliance, and developers who move fast without leaking keys. When you want AI agents that are powerful and governed, talk to the ITECS team.
